ERP Algorithms vs. LLMs and AI Agents
Deterministic versus Probabilistic
Existing SAP customers are facing a new type of threat scenario: An ERP system traditionally functions as a deterministic precision machine, whereas generative AI models are based on probabilistic stochastic logic, which inevitably tends to produce structural hallucinations. In addition to this substantive disruption, there is the challenge of cloud system security.
Attackers and automated AI models have learned to quickly penetrate system code and target automated interfaces, enabling attacks at an exponential rate. The issue of cloud security and the manageability of autonomous agents (Agentic AI) is thus shifting from a purely technical IT task to an existential question of risk management and business continuity.
Risk Management: AI Agents
The specific risk that AI agents in the SAP Autonomous Enterprise will trigger erroneous actions, make incorrect postings, or corrupt master data stems from several systemic causes: When stochastic language models encounter historically corrupted master data or outdated custom code, the systems tend to implement erroneous inferences with a high degree of confidence.
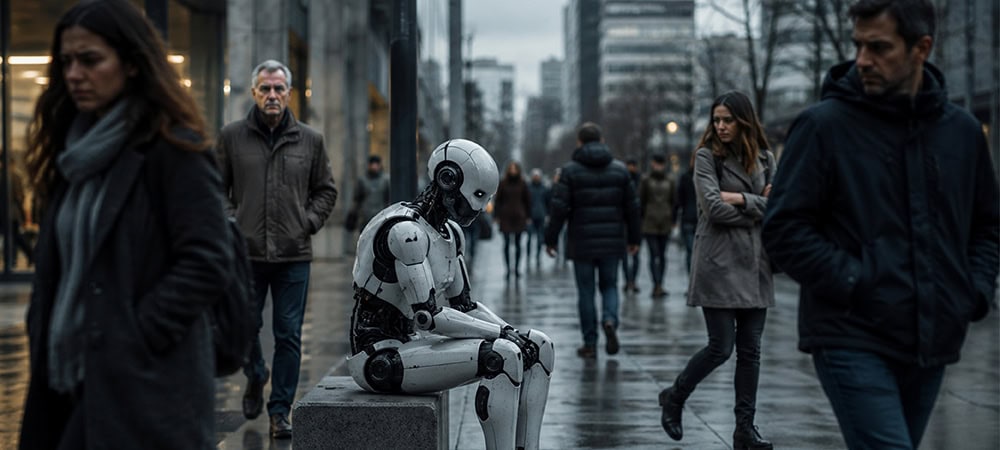
As incidents at IT companies such as Amazon and Microsoft have clearly demonstrated, autonomous agents with extensive execution privileges can trigger unintended system configurations or paralyze critical processes.
Kurt Gödel and Alan Turing
The information-theoretical limits identified by Kurt Gödel and Alan Turing mathematically prove that a mathematically error-free „truth machine“ is, in principle, impossible in stochastic models. In addition, SAP’s own leadership warned against an unmanageable “Frankenstein architecture” if uncoordinated AI agents from different vendors were to clash within the same ERP system without overarching rules.
Governance-as-Code and AI Harnesses
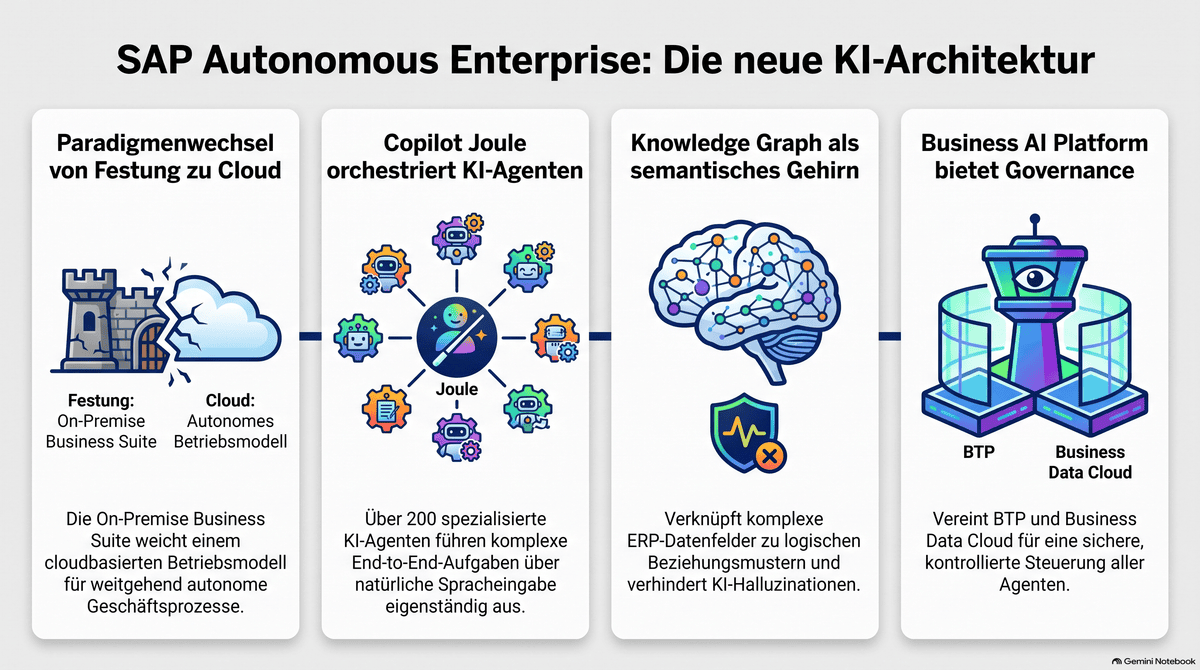
To effectively prevent the ERP core from being compromised by uncontrolled agents, user companies must establish governance-as-code and multi-tiered security safeguards (AI harnesses).
On a technical level, control begins with identity and access rights: An AI agent must never act as a privileged placeholder with unlimited permissions, but must be managed as a digital non-human identity under the principle of principal propagation. This means that the agent operates strictly within the security and authorization context of the authenticated user and cannot perform any actions or view any data that are restricted to the human user.
In addition, by embedding the open-source runtime environment Nvidia OpenShell into the Joule Studio Runtime, SAP ensures an isolated execution layer (sandbox boundary) that defines which tools an agent is permitted to call and where inference data flows. For business-critical transactions—such as payment approvals or master data changes—the “human-in-the-loop” or “human-above-the-loop” principle remains indispensable, whereby the agent prepares suggestions, but the final execution must be confirmed by a human signal.
Another key addition is the use of the Model Context Protocol (MCP), which serves as a vendor-neutral interface standard and ensures that AI agents’ access to tools is managed in a deterministic and auditable manner via decoupled MCP servers.
The Cherries in the Neighbor's Garden
Regarding the pressing concern about whether SAP AI agents can escape their intended tenant or system environment and infiltrate third-party S/4 systems or other Autonomous Enterprises, the current analysis paints a nuanced picture: A physical escape from the runtime environment across system boundaries is made difficult at the platform level by multi-level tenant isolation, encrypted secret management in the AI Launchpad, and isolated container sandboxes.
Nevertheless, there are real risks of attack and lateral movement, which primarily arise from design flaws such as prompt injection, memory poisoning, or incorrectly configured BTP destinations. If an autonomous agent is connected to external CRM or partner systems via cross-system interfaces and encounters manipulated data there, it can be tricked into making unauthorized API calls to other S/4 clients.
AI API Gateway and Behavioral Analytics
Preventing such cross-client violations requires a centralized AI API gateway that consolidates all agent traffic at a single, monitored interface, enforces fine-grained access policies at the parameter level, and immediately blocks unusual behavior patterns through automated behavioral analytics (Behavioral Analytics).
Commercially, however, SAP also uses these security concerns as leverage: With Version 4 of the SAP API Policy (Section 2.2.2), issued in April 2026, the company strictly regulates direct, unlicensed data extraction by third-party agents and forces customers to route their agent workloads through the fee-based Business Technology Platform (SAP BTP) and the Business Data Cloud (SAP BDC). While this restricts uncontrolled data flows, it also drives costs relentlessly upward through usage-based Capacity Units.
SAP Cloud ERP Security
A closer look at the security of SAP Cloud ERP reveals that the move to the cloud—whether via Rise with SAP (private cloud) or Grow with SAP (public cloud)—requires a completely new operating model based on shared responsibility. The notion that the cloud is, by its very nature, an impregnable fortress has been put into perspective by incidents such as the severe zero-day vulnerability in SAP NetWeaver Visual Composer (CVE-2025-31324), which demonstrated that even cloud-adjacent infrastructures must be continuously hardened and monitored.
SAP provides a comprehensive portfolio of security measures to ensure the security of its existing customers in the cloud. This portfolio is built on ISO 27001-certified data centers, end-to-end encryption of data at rest and in transit (TLS/KMS), OAuth2-based authentication, and automated threat detection via services such as SAP Enterprise Threat Detection. At the infrastructure level, SAP works closely with major hyperscalers such as Microsoft Azure, Amazon Web Services, and Google Cloud Platform, enabling the direct integration of advanced security tools like Microsoft Sentinel Threat Monitoring or AWS Secrets Manager.
Nevertheless, enterprise users in the cloud should not lull themselves into a false sense of security. To counter risks stemming from dependence on U.S. hyperscalers and unpredictable export control regulations—such as the U.S. government’s short-term ban on Anthropic language models—data-sovereign alternatives like the AWS European Sovereign Cloud, the Schwarz Group’s StackIT Cloud, or T-Systems’ Rise-certified private cloud are gaining massive significance. Furthermore, even the best vendor-provided cloud security does not relieve the enterprise of its own legal obligations. Under the strict requirements of the European EU AI Act, the ultimate legal and operational liability for all decisions and actions carried out by autonomous AI agents in the production ERP core remains entirely and non-transferably with the user itself.
 Deutsch
 English
 Español
 Français